Hardware / Practical guide
IT hardware procurement: evaluate the full lifecycle before buying
A lower quotation can conceal higher support costs, missing licences or equipment that is difficult to maintain.
Start with the service the equipment supports
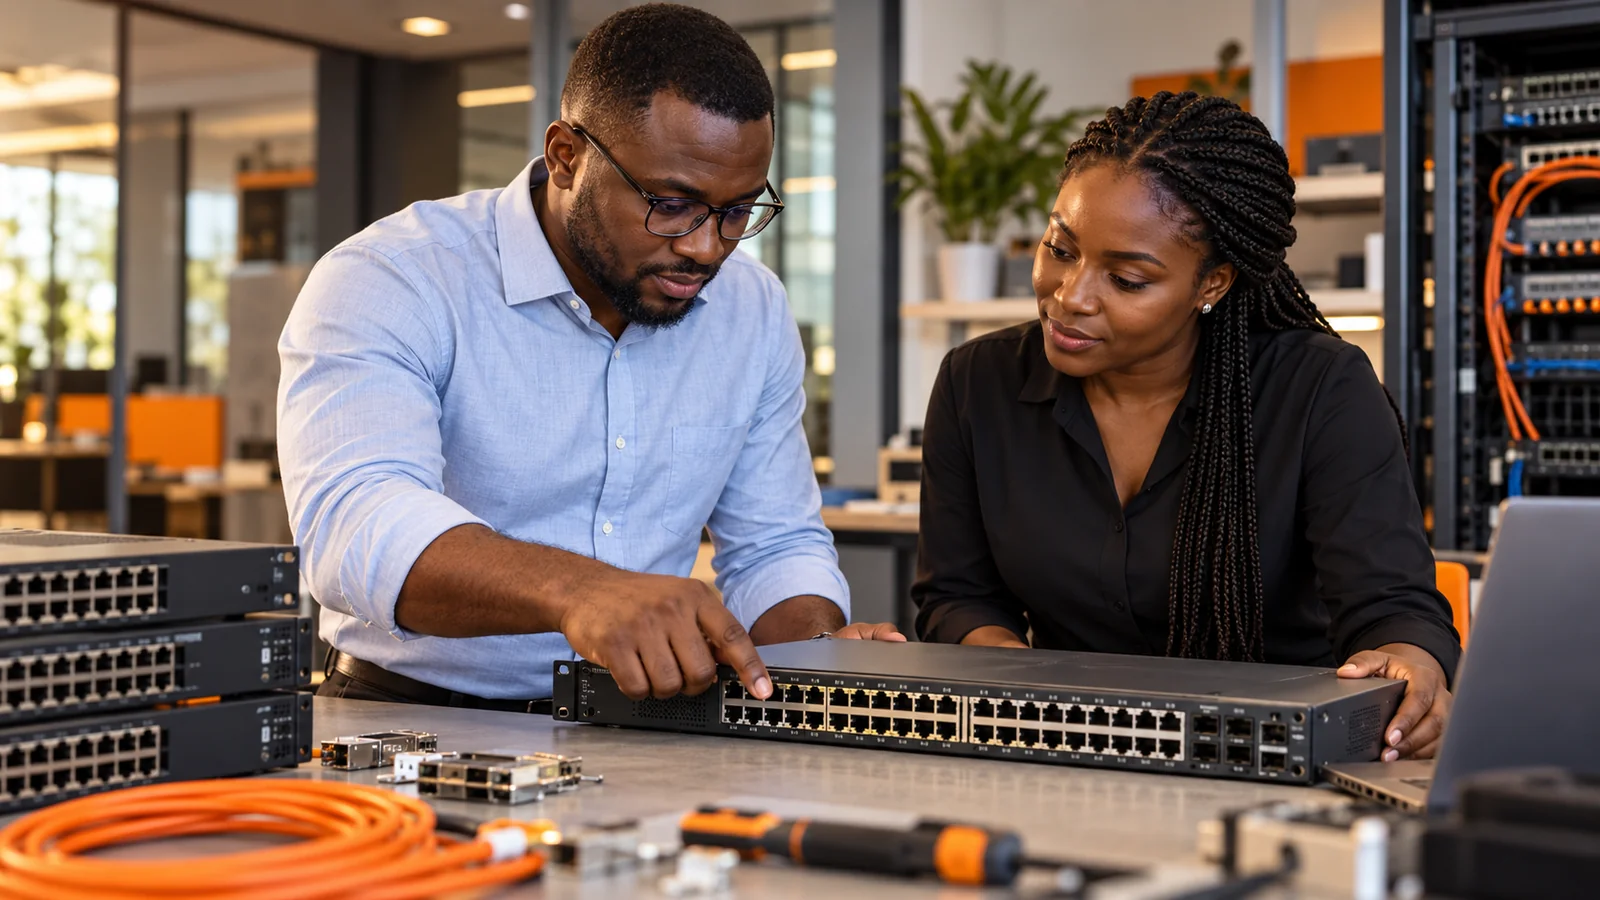
Buying a server, firewall or switch is an operational decision as well as a purchasing exercise. A device must fit its workload, environment and support model for the period the organisation expects to use it. A quotation that omits installation dependencies can make a superficially cheaper option more expensive to operate.
NIST's cybersecurity supply-chain guidance addresses risks associated with acquiring and using products and services, including concerns such as counterfeit components and poor development or manufacturing practices. [1] The buying checklist below applies that general concern to practical procurement decisions. It is not a claim that a specific product or supplier has failed an assessment.
Write a requirements sheet before requesting quotes
Describe the workload, expected growth, interfaces, availability needs and physical installation constraints. For a switch, this may include port types, uplink requirements, power delivery and management integration. For a server, specify the application requirements and supported configurations rather than choosing solely from processor or memory headlines.
Separate essential requirements from preferences. Ask the operational team to explain what happens if a requirement is missing. This prevents optional features from crowding out necessities such as compatible optics, supported storage controllers or an appropriate replacement service. Require bidders to identify exceptions explicitly instead of hiding them in a generic datasheet.
Price the complete system
Compare quotations using the same bill of materials. Include accessories, transceivers, rails, cables, licences, subscriptions, installation, delivery, taxes and support where applicable. Confirm what happens when a subscription expires and whether essential functionality, updates or management access depends on renewal.
Add the costs of power, cooling, space and staff time to the business case where material. Do not assume that the more efficient device on paper will automatically produce a particular saving in your environment. Use workload and operating assumptions that both finance and IT can understand, and show sensitivity to growth or exchange-rate exposure when relevant.
Check support life and the route to assistance
Ask for the vendor's published support position for the exact model and software combination. Distinguish warranty coverage, software updates, technical assistance and physical replacement. A next-business-day dispatch commitment is not necessarily a promise that a working service will be restored the next day.
Confirm where replacement stock is held, which locations are covered, and who handles installation or configuration after a failure. For critical equipment, compare the cost of local spares with the practical consequences of waiting. Record renewal dates and support identifiers in the asset register so they are accessible during an incident.
Validate supplier and equipment evidence
Use an appropriate sourcing channel and ask how authenticity and entitlement will be established. Record serial numbers, purchase documents and relevant licence information on receipt. Check packaging and delivered quantities against the order, and resolve discrepancies before moving the equipment into service.
A risk-based assessment should also consider firmware support, vulnerability notifications and how the supplier handles security concerns. Ask what information is available about product components and updates, but do not confuse the presence of a document with proof that every supply-chain risk has been removed. Material concerns need an accountable decision before acceptance.
Make acceptance a controlled activity
Prepare a short test plan using the actual intended configuration. Confirm that the equipment boots, recognises installed components, receives supported updates and integrates with monitoring and identity controls. Test resilience features where they are part of the requirement. Keep results and configuration backups with the asset record.
Avoid discovering compatibility problems only during the final production cutover. Where possible, stage equipment in a controlled environment and rehearse migration. Specify who can approve substitutions and what triggers rejection or remediation. Protect existing service availability while testing a new device; a procurement acceptance test should not become an uncontrolled outage.
Plan ownership through retirement
Assign responsibility for patching, configuration, renewals and disposal before handover. Record the expected review date and the conditions that would trigger replacement, such as unsupported software or a workload exceeding the agreed capacity. Plan how data-bearing components will be sanitised or destroyed using a method appropriate to their technology and sensitivity.
Evo's Hardware Procurement service combines sourcing with technical oversight. Bring the service requirements and existing architecture to the buying process so equipment, licensing and support are evaluated together. A clear acceptance record and lifecycle owner make the purchase easier to defend and the environment easier to support.
Frequently asked questions
Is warranty the same as operational support?
No. Verify the separate terms for repair or replacement, software updates, technical assistance and restoration of the business service.
What should accompany the delivered hardware?
An agreed bill of materials, entitlement and serial-number records, configuration documentation, acceptance results and named lifecycle owners.
Sources & further reading
Primary sources checked on 2026-10-18. The implementation checklists are editorial recommendations; source publications retain their original dates.